How the DORA text is structured
The Digital Operational Resilience Act is a long and complex piece of European legislation. It runs to 53 articles and 11 annexes, in six parts. Its aim is to strengthen the digital resilience of the financial sector. Adopted in December 2022, it becomes enforceable on 1 January 2025.
Who does the DORA regulation apply to?
What objectives does the DORA text set?
DORA sets out to:
- Strengthen the ability of financial entities to withstand major IT incidents, such as cyberattacks or system failures.
- Harmonise supervisory rules on digital resilience across the European Union.
- Improve communication between supervisory authorities and financial entities.
How does the DORA text put those objectives into practice?
To reach them, DORA requires financial and banking players to put various measures in place: mapping their information systems, assessing cyber risks, taking the steps needed to face potential cyberattacks, running resilience tests and, above all, monitoring data leaks in open sources (OSINT).
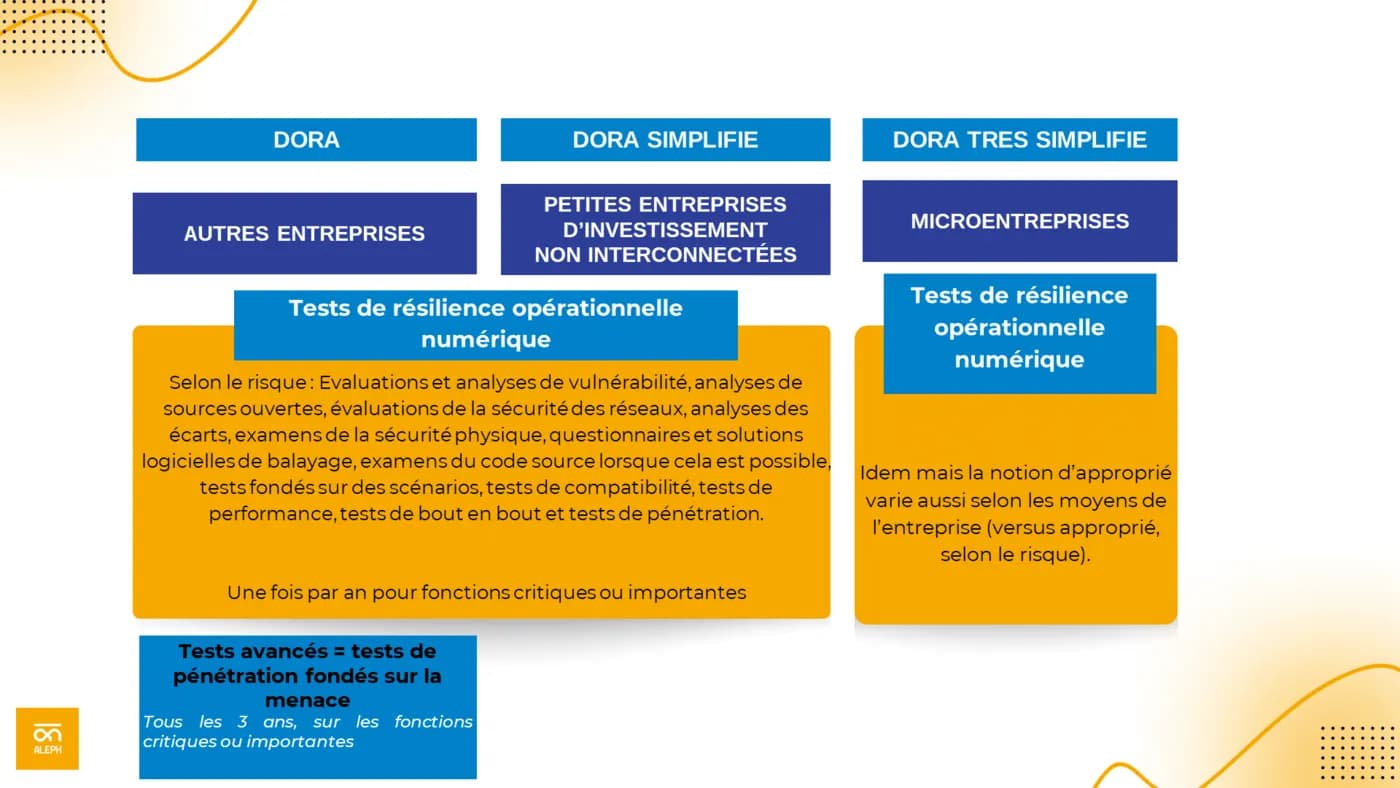
Which tests apply, by company size.
Discover Aleph Alert, the data leak alerting dashboard, built for every company.
DORA: a cybersecurity requirement
DORA puts the emphasis on cybersecurity. It requires financial entities to put measures in place to protect their IT systems against cyberattacks. Those measures include:
- Enforcing strict access controls.
- Using encryption technologies.
- Updating software regularly.
- Training staff in cybersecurity.
- Monitoring OSINT data.
- Monitoring their suppliers’ data leaks.
Data leaks, a key point in the DORA text
DORA addresses data leak monitoring in several ways:
- Detecting incidents:
DORA requires financial entities to put monitoring systems in place to detect security incidents, data leaks included.
- Investigating incidents:
It also requires financial entities to investigate in order to establish where the cyberattack came from. They must also know which data was leaked.
- Notifying authorities and sharing information:
Financial entities must notify the competent authorities in the event of a data leak — which is why investigating incidents is mandatory. They must also share cyber threat information with other financial entities.
- Penalties:
Failing on any of these points required by the DORA text leads to substantial penalties.
Read the article: how DORA comes into force
DORA is a significant challenge for financial entities, but it is also an opportunity for them to improve their risk management and strengthen their customers’ trust.
Read the article: DORA — IT resilience in the banking and financial sector